Geoff Sandoval

Software Developer · Aspiring Penetration Tester

Portrait of Geoff Sandoval

Software Developer · Aspiring Penetration Tester

Scroll

Based in Philippines

670+Commits on featured projects
480API endpoints across projects
186Automated API tests (Tugon)
100%Curiosity

(01) Mission

I build software that feels effortless — then I try to break it. The best developers think like attackers.

(02) What drives me

Build. Break. Secure.

01

Build

Full-stack web and mobile apps with React, Next.js, Flutter and Python APIs — fast and built to last.
02

Break

Ethical hacking in labs and CTFs: recon, exploitation, privilege escalation. Learning how systems fail.

03

Secure

Hashed credentials, rate limits, role guards and least privilege — security designed in, not bolted on.

(03) The story

Chapter 01

The Student

BS Information Technology. Weekly system-administration labs taught me how real systems run — and how they break.

Chapter 02

The Builder

Late nights turning ideas into shipped software: an emergency-response platform, a scholarship system, an artisan marketplace.

Chapter 03

The Breaker

Now training as a penetration tester. Every system I build, I want to know exactly how it could fall.

(04) What I do

Services & community

Development

  • TypeScript
  • JavaScript
  • React
  • Next.js
  • Flutter
  • Python
  • FastAPI
  • Flask
  • PostgreSQL
  • Redis
  • Supabase
  • Three.js
  • Git
  • System Administration

Security

  • Linux
  • Networking
  • Nmap
  • Burp Suite
  • OWASP Top 10
  • Wireshark
  • TryHackMe / HTB

(05) Featured work

Welcome to the lab.

4 builds — from cinematic front-ends to enterprise infrastructure — each with the stack, techniques and security decisions behind it.
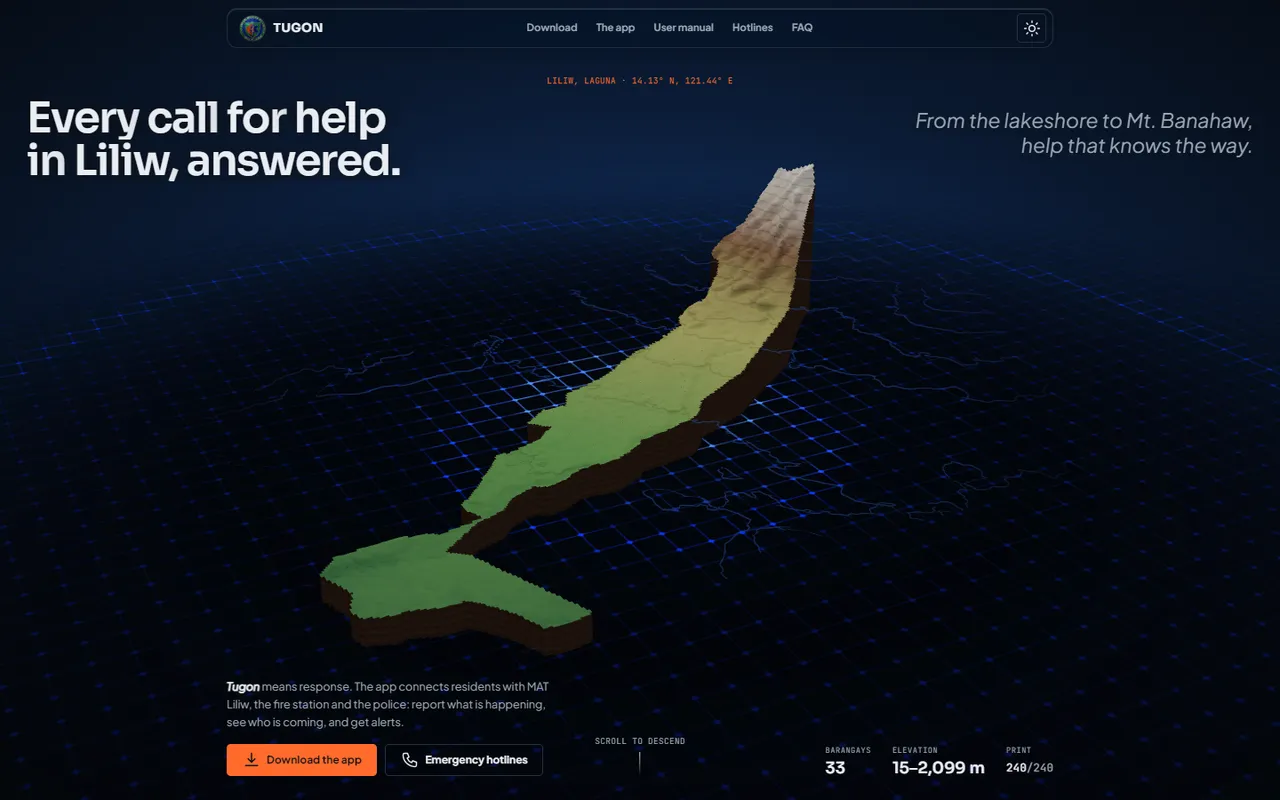
Tugon preview

01 / 04Mobile App + Admin Dashboard · Emergency response · 2026

Tugon

Full-stack developer · team of 2 · ~64% of commits

Emergency-response platform for the municipality of Liliw. Citizens report incidents from the mobile app; staff dispatch and track responders live from a web command center, and AI helps triage reports.

API endpoints
216
Mobile screens
58
Admin pages
70
User roles
10
  • Flutter
  • Dart
  • FastAPI
  • Python
  • Next.js
  • TypeScript
  • PostgreSQL (Supabase)
  • Prisma
  • SQLAlchemy
  • Redis
  • Firebase Cloud Messaging
  • Gemini API
  • Leaflet / Google Maps
  • Render

Features

  • Citizens report incidents with photos and voice input
  • Web command center: dispatch, live tracking, incidents and evacuation
  • Separate officer portal for patrols, attendance and reports
  • Live responder tracking on a map over WebSockets
  • Mission dispatch with push notifications; GPS and face-match attendance
  • AI report triage with descriptive and predictive analytics

Techniques

  • Async FastAPI with a pooled, pre-warmed PostgreSQL connection
  • Admin on Next.js with Prisma (34 models), TanStack Table and Recharts
  • Redis rate limiting with an in-memory fallback
  • TTL response cache that is invalidated on writes
  • Multi-provider AI router with priority and cooldown fallback
  • 186 automated API tests with pytest

Security

  • bcrypt password hashing
  • JWT sessions with an active-account check on every request
  • Role-based guard on 39 admin endpoints; admin routes split by role
  • Session JWT kept in an httpOnly cookie, forwarded server-side
  • Per-IP and per-account rate limits on login, signup and OTP
  • Hashed, expiring email OTPs capped at 5 attempts

02 / 04Web App · Scholarship management · 2026

Applischo

Full-stack developer · solo project

Scholarship management system for a municipal program, from application and exam to evaluation, approval and payout. A rule-based scorer recommends; staff decide.

API endpoints
155
Database tables
34
User roles
5
  • Next.js 15
  • React 19
  • TypeScript
  • Tailwind CSS 4
  • PostgreSQL (Supabase)
  • Supabase Storage
  • Resend
  • MediaPipe
  • Vercel

Features

  • Applicants build a profile and see rule-by-rule eligibility
  • Online exams with a timer, anti-cheat flags and a camera check
  • Weighted, explainable scoring that staff can adjust with a reason
  • Authority approves, returns or rejects, with bulk approval
  • Renewals, payout batches and claim tracking for scholars

Techniques

  • Eligibility rules stored as data and run by one pure rule engine
  • Weighted scoring with anomaly flags and plain-language reasons
  • Application workflow defined in a single transition table
  • Fuzzy duplicate detection using a Dice similarity score
  • Server-owned exam clock with a disconnect policy

Security

  • bcrypt password hashing
  • Signed httpOnly session cookie, rechecked against the database per request
  • Role-based access in middleware and on API routes
  • OTPs stored as keyed hashes, 10-minute expiry, 5 tries
  • Parameterized SQL, Row Level Security, AES-256-GCM for stored API keys

03 / 04E-commerce · 3rd-year project · 2025

Eterna

Full-stack developer · solo build

Marketplace for local artisans with separate buyer, seller, rider and admin portals. Includes checkout, a commission wallet, live chat and an AI shopping assistant.

API endpoints
109
Pages
33
User roles
4
  • React 19
  • TypeScript
  • Redux Toolkit
  • Tailwind CSS 4
  • MUI
  • Flask
  • PostgreSQL
  • Socket.IO
  • Cloudinary
  • PayPal

Features

  • Buyers browse products, check out and track orders
  • Seller portal for products, orders and analytics
  • Rider portal for deliveries, with order QR codes from checkout
  • Real-time chat between buyers, sellers and riders
  • AI shopping assistant that answers from the live product catalog

Techniques

  • Feature-based modules on both the React app and the Flask API
  • Access and refresh tokens signed with separate secrets
  • Wallet ledger with a configurable commission on each order
  • Socket.IO rooms for real-time messaging
  • Admin approval workflow for new users, sellers and riders

Security

  • bcrypt password hashing
  • Parameterized SQL queries throughout
  • Role guards for buyer, seller, rider and admin API routes
  • Email OTP verification with a 5-minute expiry
  • Secrets and API keys read from environment variables

04 / 04System Administration · ITEP 414 · 2026

System Administration Portfolio

Coursework · solo

A semester-long lab portfolio: planning the enterprise infrastructure of a 20-person startup, then deploying, networking and securing Ubuntu and Windows servers — every step documented.

Employees planned for
20
Server OSes deployed
2
Backup strategy
3-2-1
  • Ubuntu Server 22.04 LTS
  • Windows Server
  • OpenSSH
  • DHCP
  • Virtual machines
  • Microsoft Defender
  • draw.io
  • Linux CLI

Features

  • Enterprise infrastructure plan for QWERTY Solution Inc. (20 staff, 4 departments)
  • Network topology: ISP → firewall → router → core switch → department LANs
  • Ubuntu Server and Windows Server VMs installed and configured
  • OpenSSH remote access and DHCP networking, verified end to end
  • BIOS vs UEFI research and a Linux boot sequence flowchart

Techniques

  • Requirements-driven planning per department and headcount
  • VLAN segmentation and redundancy design: SLA fiber, LTE failover, RAID
  • Manual disk partitioning and CLI package management
  • Professional technical writing: installation guide and manual

Security

  • Perimeter firewall plus VLAN isolation between departments
  • Least privilege, regular patching, MFA and a password manager (NIST SP 800-63B)
  • 3-2-1 backups following CISA guidance
  • Remote administration over encrypted SSH; servers patched right after install
More on GitHub — github.com/sandoval02 ↗

Let's build something secure.

hello@gpscrypt.me